Modern digital platforms occupy the absolute core of contemporary commercial ecosystems, where every click, scroll, and transaction generates data that powers core business models. This structural shift has successfully transformed data governance from a routine back-office compliance chore into a vital consumer protection discipline in its own right. When a platform mishandles personal information, the resulting harm is rarely abstract or purely theoretical; instead, it immediately manifests as manipulated consumer choices, unfair pricing tiers, sudden service denials, identity theft, or the quiet, frustrating loss of control over one’s own digital footprint. This definitive operational guide establishes a rigorous, actionable framework for platform governance that genuinely shields consumers rather than simply satisfying a bureaucratic checklist.
Why Data Governance Is a Consumer Protection Issue
Traditional privacy statutes are frequently written in the dense language of formal compliance: lawful processing bases, rigid retention schedules, and exhaustive records of processing activities. However, the fundamental legislative purpose behind these rules is consumer welfare. A user who cannot comprehend what data is actually collected can never provide meaningful, informed consent. A user who is locked out of correcting an erroneous record may find themselves wrongly denied credit, housing, or professional employment. Framing data governance as a tangible consumer outcome rather than a static legal formality fundamentally changes how product teams prioritize engineering sprints, measure success, and escalate operational friction that looks minor on a corporate dashboard but severely impacts a real person’s daily life.
The Regulatory Baseline: From Consent to Accountability
Today, multi-market platforms operate under a complex web of overlapping regulatory regimes. Europe’s GDPR and its UK counterpart established the global compliance template, focusing heavily on purpose limitation, strict data minimisation, and organizational accountability. California’s CCPA, as significantly amended by the CPRA, introduced comprehensive consumer opt-outs for data sharing and sales, while Brazil’s LGPD, Singapore’s PDPA, and a steadily expanding wave of national privacy laws follow a remarkably similar structural logic. Sector-specific rules for financial services and healthcare add intense extra layers of oversight. Furthermore, platform-specific legislation such as the EU Digital Services Act (DSA) and Digital Markets Act (DMA) pushes the envelope further, demanding absolute transparency regarding targeted advertising, algorithmic recommender systems, and secure data access for academic researchers and regulatory watchdogs.
The pragmatic operational implication is clear: engineering your platform architecture to meet the strictest applicable global standard is invariably cheaper and safer than maintaining fragmented, parallel compliance workflows. A unified global data inventory, a single centralized consent management architecture, and a streamlined rights-handling pipeline will service virtually every geographic market while remaining resilient against inevitable future legislative updates.
Map the Data Lifecycle Before Writing Policy
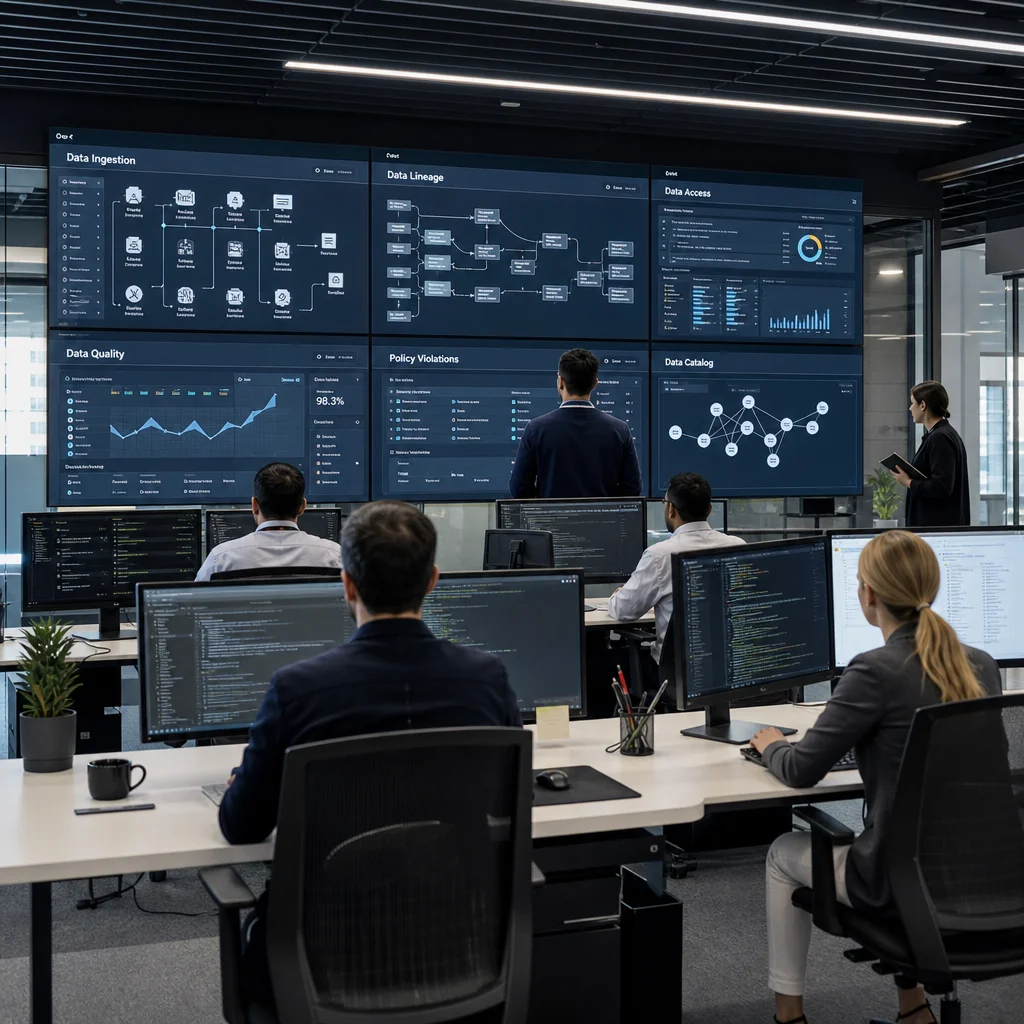
Corporate policies consistently fail when they describe an idealized organization that does not exist in practice. Successful governance always starts with a forensic, factual map of how personal data actually moves through the platform infrastructure, attaching strict technical controls to every distinct stage of the lifecycle.
- Collection: cataloguing precisely what data is gathered, from which specific user interface, and under what documented legal basis.
- Storage: mapping exactly where records live, enforcing strict role-based access queries, and ensuring end-to-end encryption at rest and in transit.
- Use: identifying which product development, marketing automation, and business analytics teams touch the data and verifying their operational purpose.
- Sharing: auditing every third-party processor, advertising exchange partner, and embedded software development kit (SDK) that receives a data copy.
- Retention: defining exact operational lifecycles, expiration dates, and verifying what technical mechanisms actually purge the records.
- Deletion: ensuring data erasure reliably propagates across immutable backups, operational server logs, and actively trained machine learning models.
Consent That Actually Means Something
Consent has historically been the most abused and corrupted concept in digital product operations. Interface dark patterns that make “accept all” a glowing, prominent button while hiding “manage preferences” behind a faint grey link do not produce legally valid or morally sound consent, a reality regulators are enforcing with severe financial penalties. Meaningful consent demands an uncompromised, genuine choice, granular processing purposes written in plain language, and a withdrawal mechanism that is just as visible and frictionless as the opt-in path. Crucially, the platform’s underlying microservices must wire this consumer choice into real-time operational execution. A consent log that is disconnected from the ad-tech stack, the CRM database, and analytics pipelines represents paperwork, not true governance.
Notice Design and Transparency
True transparency is never achieved by publishing a longer, unreadable privacy policy. Instead, it is measured by an ordinary consumer’s ability to answer three basic questions within sixty seconds: what data do you collect, why do you need it, and who else gets to see it? Layered notices, concise in-product explanations deployed precisely at the moment of collection, and plain-language summaries of complex data-sharing arrangements consistently achieve superior comprehension compared to traditional legal documents that users invariably skip. Where sophisticated algorithms are deployed to personalize pricing structures, rank product offers, or generate behavioral risk scores, the platform must explain the core logic in clear terms and provide an explicit pathway for human review and challenge.
Algorithmic Decisions, Profiling and Fairness
Algorithmic recommender systems and automated profiling engines sit at the volatile intersection of technical data governance and consumer protection. Machine learning models trained on historical datasets will inevitably reproduce historical biases and social disadvantages unless engineering teams deliberately test for and mitigate these skews. Effective governance requires comprehensive model cards, rigorous bias testing across protected and proxy demographic attributes, mandatory human-in-the-loop review for automated decisions carrying significant legal or financial effects, and a clear explanation pathway for users who are systematically ranked, priced, or excluded. Maintain a centralized registry of all high-risk models, record their underlying training data provenance, and schedule mandatory re-assessments rather than waiting for public consumer complaints or investigative journalism to force an audit.
Rights Requests, Complaints and Breach Response
Consumer trust in digital infrastructure is ultimately built or destroyed in how individual edge cases are handled. Data subject access requests (DSARs), correction orders, deletion mandates, portability requests, and formal objections must flow through a single, fully tracked ticketing queue governed by published, enforceable turnaround SLAs. Consumer complaints regarding data mishandling deserve the exact same operational rigor as financial payment disputes.
- Verify user identities proportionately, avoiding abusive demands for excessive identity documentation.
- Log every single request, the final compliance decision, and the precise operational reasoning behind it.
- Escalate systemic anomaly patterns, rather than treating issues as isolated tickets, to the executive governance forum.
- Run realistic incident breach drills that actively test customer communication workflows, not just internal legal notifications.
Third Parties, Vendors and Data Sharing
The vast majority of severe data security incidents originate through third-party supply chain vulnerabilities. Advertising SDKs, enterprise cloud providers, analytics vendors, and outsourced customer support platforms instantly expand your operational data perimeter. Legal contracts are entirely necessary but fundamentally insufficient on their own. Require exhaustive security questionnaires prior to vendor onboarding, enforce strict principle-of-least-privilege access controls, continuously monitor for scope creep, and maintain a definitive asset inventory assigning a named internal owner to every single platform integration. When a commercial partner alters their terms of service or a plugin remains dormant for months, treat that as a mandatory trigger to audit or strip out the integration, rather than letting it quietly execute in the background of a live production environment.
Dark Patterns and Interface-Level Governance
Many modern consumer harms are deliberately engineered design decisions rather than accidental data leaks. Difficult-to-cancel subscription renewals, pre-checked opt-in boxes, confusing double-negative interface language, and manipulative notification prompts that shame users into surrendering extra data are all core data governance issues because they systematically undermine informed consumer autonomy. The operational remedy is strictly procedural: review all user onboarding and purchasing flows for manipulative dark patterns before code deployment, involve legal compliance and UX research teams in design critiques, and treat interface dark patterns as an actionable compliance risk with a designated owner and measurable reduction targets.
Metrics That Reveal Real Risk
Traditional corporate reporting often relies on vanity metrics, such as the total number of policies published or mandatory training sessions completed. These numbers rarely correlate with actual risk reduction. Instead, management must measure operational variables that accurately predict consumer harm:
- Median time required to fulfill a data access or deletion request, broken down by geographic market.
- Percentage of platform data assets possessing a clearly assigned internal business owner and documented processing purpose.
- Total volume of active third-party integrations and the exact percentage reviewed within the current quarter.
- Consumer consent withdrawal velocity and the precise technical propagation speed to downstream marketing databases.
- Proportion of high-risk algorithmic models subjected to independent fairness and bias reviews within the last twelve months.
Governance Structure: Who Owns What
Organizational accountability requires a designated leader, an allocated budget, and a strict operational calendar. A highly functional governance model pairs a centralized privacy and data compliance function with embedded data stewards stationed directly inside product development, engineering, marketing, and customer support divisions. A cross-functional governance council should meet monthly to review core risk metrics, approve high-risk data processing activities, and close audit findings. Executive leadership must actively sign off on the corporate risk appetite, receive quarterly reports written in plain business language, and be notified within hours of any security or privacy incident likely to impact end consumers. Boards of directors that only discover data failures when regulators initiate public enforcement actions are not governing—they are merely reacting.
Common Failure Modes
- Treating data governance as a static documentation project that permanently concludes the moment a policy document is signed.
- Isolating consent management within the legal department while the live ad-tech stack operates on entirely autonomous technical logic.
- Discovering dangerous “shadow data” trapped in unmanaged spreadsheets, localized support tools, and marketing lists only when an external audit begins.
- Applying strict data retention rules exclusively to primary production databases while ignoring neglected backups, logs, and historical data warehouses.
- Assuming that a third-party vendor’s standard compliance certification automatically transfers legal and ethical responsibility for consumer harm away from your platform.
A Practical Maturity Path
Product teams embarking on this journey should focus their initial phase on three foundational pillars: establishing a comprehensive inventory of all personal data assets, deploying a reliable rights-request management workflow, and assigning a single operational owner for privacy execution. The intermediate maturity stage introduces automated data retention enforcement, scheduled vendor audits on a fixed calendar cycle, and consent orchestration wired natively into every marketing and analytics pipeline. Mature organizational programmes invest heavily in granular machine learning model documentation, independent third-party algorithmic audits, and ongoing user research designed to test whether privacy notices are genuinely understood by average consumers. Each progressive maturity stage drastically diminishes the statistical probability that a routine operational decision transforms into a damaging consumer complaint or a severe regulatory finding.
The Bottom Line
Effective data governance succeeds when it is executed as core product development rather than tedious administrative paperwork. Consumers ultimately judge a digital platform by a simple standard: whether it asks permission before taking action, clearly explains what it is doing with their information, and responds rapidly and transparently when something goes wrong. Regulatory frameworks, technical standards, and compliance audits matter deeply, but their sole purpose is to serve and protect that human user experience. Build the accurate inventory, wire the technical controls directly into the systems touching your customers, measure the specific operational metrics that predict harm, and empower a designated team member with the absolute authority to halt a product launch that fails the consumer protection test. That powerful combination protects users far more reliably than any compliance policy document sitting unread on a corporate website.
“