Why Regulation Finally Caught Up With Digital Play
Two decades ago, digital entertainment operated largely within a regulatory vacuum. Users could download software, stream high-definition media, or execute micropayments inside interactive environments with virtually zero institutional oversight. Governments viewed the interactive entertainment sector as a fringe novelty, too agile and fast-paced to warrant serious legislative intervention. Today, that laissez-faire era has vanished. Digital entertainment commands multi-billion-dollar revenues, positioning it alongside traditional media and financial services. Consequently, regulatory bodies have implemented rigorous compliance frameworks that govern every stage of the product lifecycle—from initial corporate licensing and server architecture to dynamic in-app economies and user verification protocols.
This regulatory pivot did not occur overnight, nor was it uniform across international borders. It followed a well-documented trajectory: initial consumer unease, sensationalized media scrutiny, formal governmental consultation papers, and, ultimately, binding statutory law. What distinguishes the contemporary regulatory ecosystem is the convergence of pressure. Child safety advocates, fiscal authorities, data protection commissioners, antitrust watchdogs, and tier-one payment processors now exert simultaneous influence on the industry. Operators can no longer isolate compliance as a backend legal concern; it is a foundational pillar of product architecture.
From Arcades to App Stores
The earliest forms of recreational regulation targeted physical infrastructure. Traditional arcades, betting establishments, and video rental storefronts required local municipal permits because they occupied physical land and engaged face-to-face with local citizens. Inspections were straightforward, and the corporate entity running the venue was transparently identified. Digital distribution shattered these paradigms. A complex multiplayer title or video-on-demand service could be deployed from a headless server cluster located in a tax-neutral jurisdiction, marketed to minors across continents, and monetized via anonymous digital wallets.
The industry’s initial response relied on self-regulation. Digital storefronts established their own terms of service and moderated digital communities through internal contractual agreements rather than public statutes. This approach functioned adequately while platforms remained relatively small and corporate reputations held tangible market value. However, this model buckled when a handful of proprietary app stores achieved gatekeeper status over millions of independent developers and billions of active users. When private technology conglomerates effectively dictate marketplace rules for the global economy, legislative bodies inevitably step in to reassert public sovereignty.
The Licensing Patchwork Nobody Designed
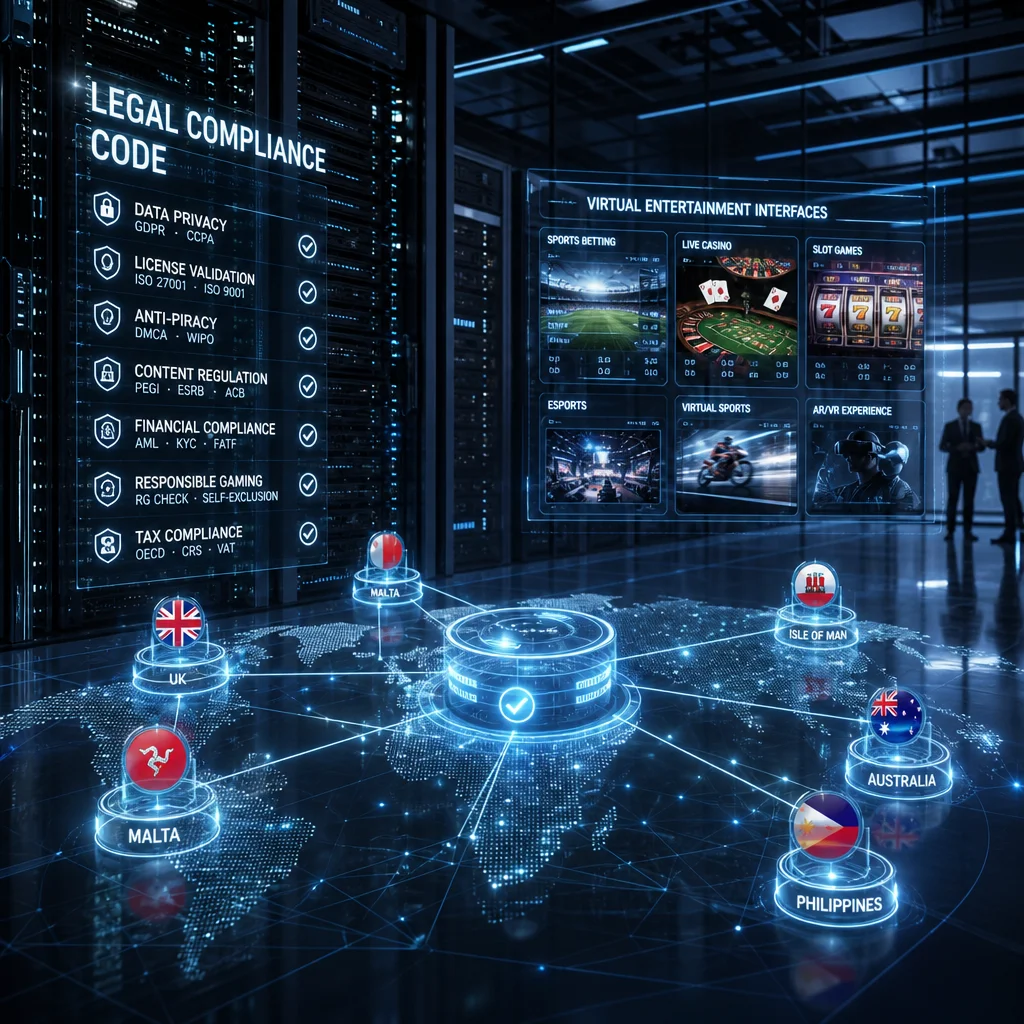
There is no such thing as a unified global entertainment licence. A digital platform operating with complete legal impunity in one territory may face severe criminal and civil penalties in another, with the underlying distinctions rarely apparent from a consumer-facing perspective. Compliance fragmentation typically manifests in three distinct ways:
Entity-Level Licensing: Certain jurisdictions regulate the corporate operator directly, mandating a localized subsidiary, a designated legal representative, and substantial financial bonds before any software deployment can occur.
Activity-Based Licensing: Other regions require specialized permits tied to specific platform functions, demanding separate authorizations for real-money transactions, live-streaming infrastructure, or user-generated content hosting.
Technology-Centric Licensing: A third category regulates the underlying software logic itself, treating any engine that facilitates paid competition, wagering, or speculative mechanics as a restricted utility regardless of who operates it.
For platform architects and legal counsels, this fragmentation breeds operational friction. Engineering a single software product to satisfy dozens of conflicting regulatory frameworks is fiscally prohibitive. Consequently, enterprises increasingly adopt a “highest common denominator” compliance strategy—designing to the strictest regulatory threshold globally and applying those rigorous controls universally. This creates an organic drift toward international harmonization, driven less by multilateral treaties and more by engineering expediency.
Age Verification Moves From Checkbox to Proof
For years, digital age gating was an exercise in compliance theater. Users simply selected a birth year from a dropdown menu, the interface accepted the input without friction, and access was granted. Regulators have systematically dismantled this facade, raising technical and legal standards significantly.
Contemporary regulatory mandates typically enforce a tiered verification model. The baseline tier permits soft authentication via behavioral heuristics and self-declaration. The intermediate tier requires cryptographic validation through trusted third parties, such as open banking APIs, mobile network operators, or sovereign digital identity schemes. The most stringent tier enforces zero-knowledge proofs, compelling platforms to verify that a user meets a specific age threshold without collecting, processing, or storing any underlying personal identity data.
This zero-knowledge approach represents a fascinating intersection of competing legal mandates. Data minimization directives demand that platforms retain as little personal data as possible, while child protection statutes mandate absolute certainty regarding user demographics. The engineering compromise is decentralized age assurance: an independent credential provider verifies the user’s status and passes a binary pass/fail token to the platform. Platforms that integrated these cryptographic primitives into their core infrastructure early on have dramatically reduced their long-term compliance overheads.
Loot Boxes and Monetization Under the Microscope
Few monetization features have attracted as much regulatory hostility as the paid randomized reward loop—commonly known as the loot box. The core legal grievance is straightforward: when consumers exchange fiat currency for a digital asset of indeterminate value, the transaction mirrors traditional speculative gambling.
Global regulatory responses have fractured into distinct models. Several European nations classify specific randomized mechanics as unlicensed gambling, requiring full gaming concessions that standard software studios cannot secure. Other territories have banned the sale of randomized items to verified minors outright. Meanwhile, a third group eschews outright bans in favor of mandatory transparency, forcing publishers to disclose statistical drop rates and implement granular spending caps. Beyond these measures, several consumer protection agencies are actively investigating whether the neuro-psychological design of these monetization loops constitutes an inherently deceptive and harmful practice.
As a result, monetization design is no longer governed solely by creative directors and game economists. Modern studios subject every economic loop to rigorous legal review prior to prototyping, fully aware that a mechanic cleared in one market may be entirely unviable—or outright illegal—in another.
Content Ratings Across Borders
Age-rating boards historically operated as insular national institutions with distinct cultural norms. A digital title could be approved for young audiences in one territory while facing total refusal of classification next door for arbitrary reasons. The rise of instantaneous digital distribution exposed the profound inefficiencies of these localized evaluation pipelines.
The gradual remedy has been the adoption of mutual recognition agreements and international coalitional frameworks. Regional rating coalitions now accept standardized classification assessments across borders, mapping disparate national criteria onto unified scoring systems. While this significantly lowers administrative overhead for large publishers, it concentrates immense influence within a few dominant rating bodies. Smaller independent studios bear the heaviest burden, as they often lack the financial resources required to navigate multi-jurisdictional submission processes.
Data Protection Meets Game Design
Interactive entertainment platforms sit atop colossal vaults of behavioral telemetry. Telemetry feeds real-time matchmaking algorithms, dynamic pricing engines, volumetric audio chats, and spatial positioning data. Modern data protection legislation—such as the GDPR and its international analogs—has systematically reframed this valuable asset class into a high-risk operational liability.
Core compliance obligations are now unambiguous: collect strictly what is necessary for platform functionality, articulate clear lawful bases for processing, retain data only for defined life-cycles, and execute verifiable data erasure upon request. The technical hurdle lies in data provenance. A single active user’s telemetry is frequently distributed across disparate systems: real-time analytics warehouses, third-party anti-cheat modules, customer support ticketing platforms, and programmatic advertising networks. Fulfilling a comprehensive deletion request demands a unified data inventory that many legacy studios never built.
Cross-border data transfers compound this complexity. Streaming player telemetry across jurisdictional boundaries requires robust contractual safeguards, localized data residency configurations, or explicit user consent. Platforms that treat data localization as an afterthought inevitably uncover architectural flaws during formal regulatory audits—arguably the most expensive moment to discover a compliance gap.
The Safe Harbour Debate
Much of the modern internet’s economic architecture rests on foundational safe harbor doctrines: platforms are insulated from civil liability regarding user-generated content, provided they execute prompt takedowns upon receiving formal notice of illegality. This legislative bargain is currently undergoing aggressive rewriting worldwide.
Emerging legal frameworks demand proactive moderation duties rather than reactive compliance. Platforms are legally compelled to perform systemic risk assessments, integrate algorithmic mitigation into their core recommendation feeds, and submit to mandatory independent third-party audits. In exchange for these onerous duties, modern frameworks offer clearer statutory liability protections than the ambiguous precedents of the past. Industry stakeholders remain deeply divided on the merits of this trade. Proponents argue that reactive moderation cannot possibly scale to billions of daily user submissions. Critics caution that ballooning compliance costs cement the dominance of market incumbents, effectively deputizing private technology companies as unelected enforcers of ambiguous public policy.
For independent developers and mid-sized operators, the essential operational takeaway is meticulous documentation. Regulators rarely penalize companies merely for encountering complex moderation challenges; they penalize organizations that fail to maintain auditable, transparent logs of how those challenges were evaluated and resolved.
Sandboxes and Co-Regulation
Recognizing the sluggish pace of traditional legislative drafting, an increasing number of regulatory authorities have deployed innovation sandboxes. These controlled environments enable tech companies to deploy emerging products under regulatory supervision, granting temporary exemptions from specific statutory requirements. The regulator gains deep empirical insight into how novel technologies behave in the wild, while the enterprise secures a viable path to market without enduring protracted legal battles.
Co-regulation follows a parallel pragmatic philosophy. Industry trade associations collaborate to draft rigorous technical standards, state authorities formally ratify them, and adherence to these voluntary standards creates a legal presumption of compliance. This hybrid model operates with greater velocity than statutory law and possesses more flexibility than pure self-regulation, though its integrity depends heavily on transparent stakeholder representation during the drafting phases.
What Comes Next
Three overarching vectors will dictate the trajectory of digital entertainment regulation over the coming decade:
Ecosystem Interoperability: Regulators are increasingly mandating open access standards, compelling dominant platform gatekeepers to allow third-party app stores, alternative payment gateways, and cross-platform messaging protocols.
Artificial Intelligence Governance: The proliferation of generative AI drastically reduces content creation costs while complicating moderation efforts. This will force regulatory bodies to mandate strict data provenance standards, mandatory watermarking, and transparent disclosure duties for synthetic media.
Enforcement Capacity: Legislative frameworks are expanding faster than the bureaucratic apparatus required to police them; future enforcement will rely heavily on automated auditing pipelines and algorithmic compliance verification.
For industry operators, the strategic mandate is clear: treat platform licensing and regulatory compliance as core product requirements rather than peripheral legal afterthoughts. Embed robust age assurance protocols, comprehensive data mapping, and immutable audit trails directly into your engineering architecture from day one. Benchmark your compliance framework against the most rigorous market you intend to serve, and design your systems to scale accordingly. The enterprises that successfully navigate continuous regulatory evolution are rarely those that accurately predict every upcoming statute; they are the organizations engineered for operational resilience and swift adaptability.
“